Solutions · Use Case

SASE and Zero Trust, delivered as one fabric

Converge SD-WAN and network security into one cloud-managed service, where identity, not location, decides who reaches what

SASE and Zero Trust on the Hermes Orchestrator
Why SASE

What SASE means on Hermes

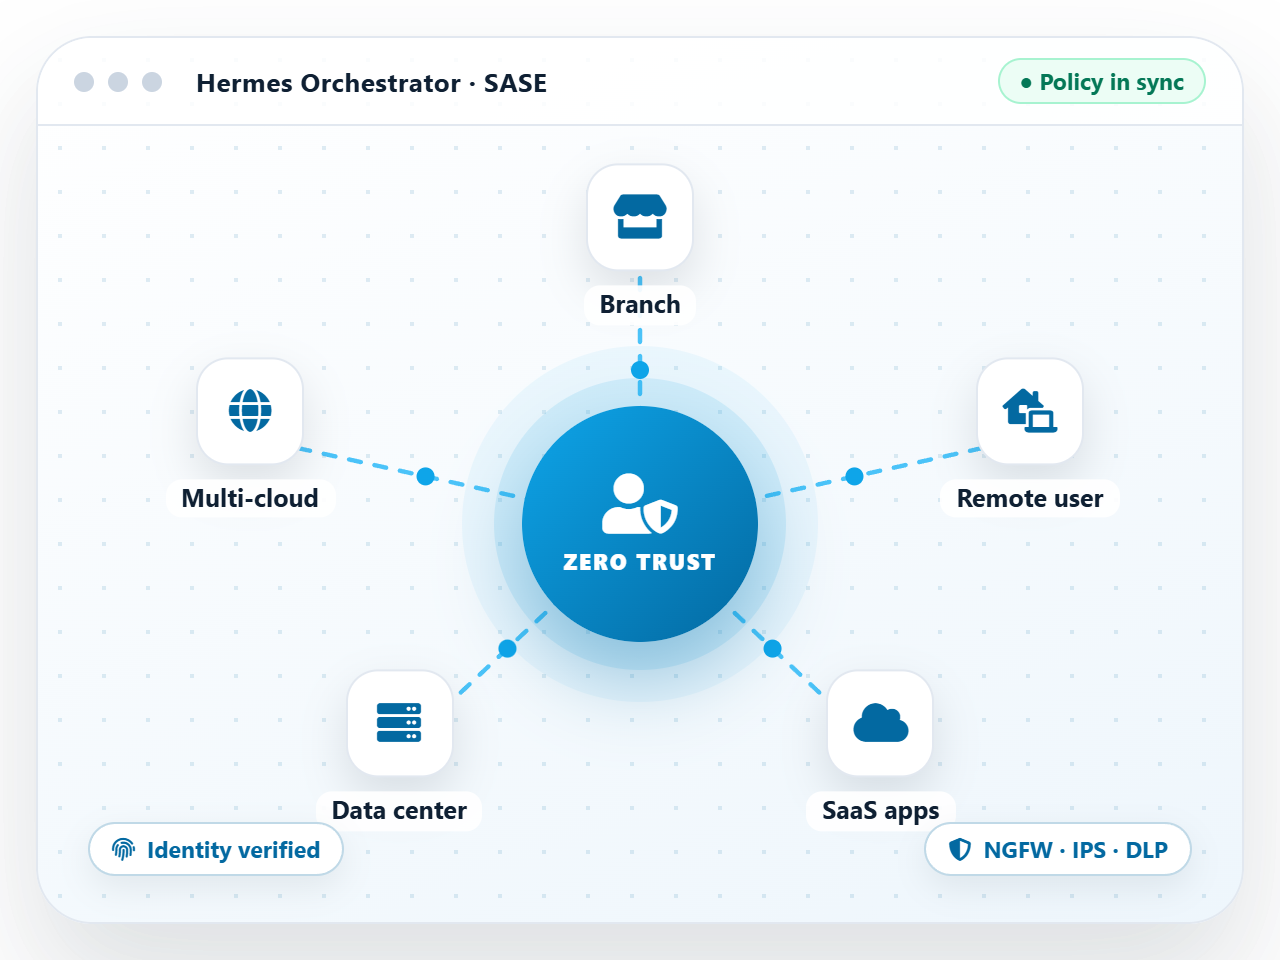
Secure Access Service Edge (SASE) brings networking and security together so every user, branch and cloud workload is protected by the same policy. Instead of backhauling traffic to a central firewall, Hermes inspects it at the edge of every site and routes it on the best available path.

Zero Trust is the access model inside that fabric. No device or user is trusted because of where it sits on the network. Every connection is checked against identity and device posture, and only gets access to the applications its role needs.
At a glance
One policy for branches, remote users and cloud
Security inline at every Hermes edge
Least-privilege access by identity and posture
Managed from the Hermes Orchestrator
Building blocks

The SASE building blocks

Every capability runs on the same edge and is managed from one console

Secure access anywhere

Broker every connection by identity and posture, whether the user is in a branch or at home.

Next-gen firewall

Application-aware firewalling at every site, configured once and pushed everywhere.

Intrusion prevention

Inline IDS/IPS inspects traffic at the edge and blocks known attack patterns.

Data protection

AI-assisted DLP keeps sensitive data from leaving through apps and uploads.

Threat intelligence

Live threat feeds update protection across the whole fleet at once.

Cloud on-ramps

Fast, secure paths to SaaS and multi-cloud through Hermes global gateways.

How it works

From first site to full SASE

1

Connect

Deploy a Hermes edge at each site. It provisions itself zero-touch from the Orchestrator.

2

Identify

Tie access to users, devices and roles instead of IP addresses and network location.

3

Inspect

Firewall, IPS, DLP and threat intelligence run inline on every edge.

4

Enforce

Write a policy once and the Orchestrator applies it to every site and user.

Hardware

Runs on Hermes hardware

Every Hermes device is provisioned zero-touch and managed from the same Orchestrator

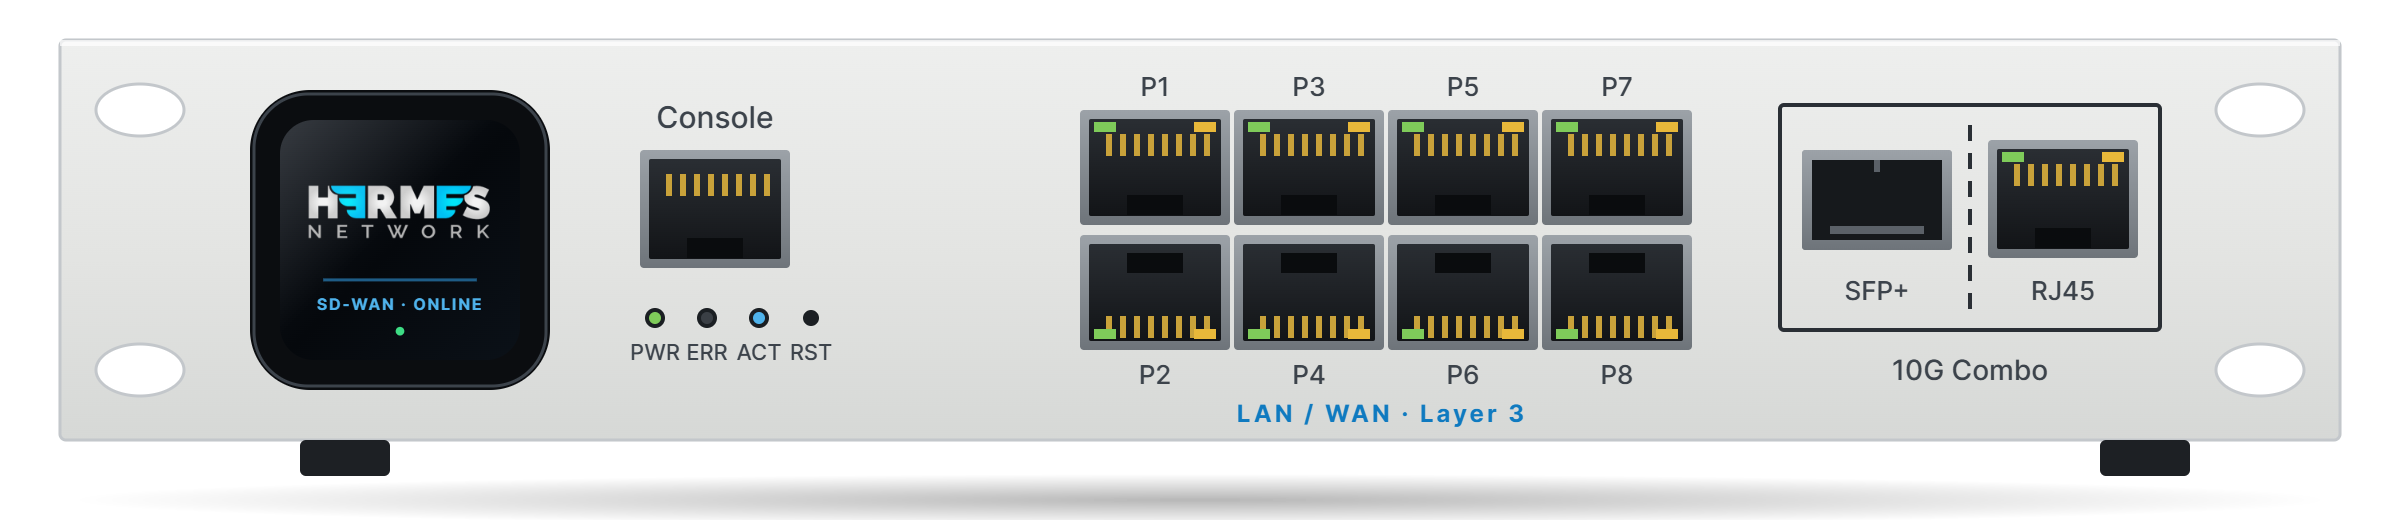
SD-WAN AI Edge Desktop

Branch SD-WAN, Layer 3 switching and edge AI in a compact desktop appliance.

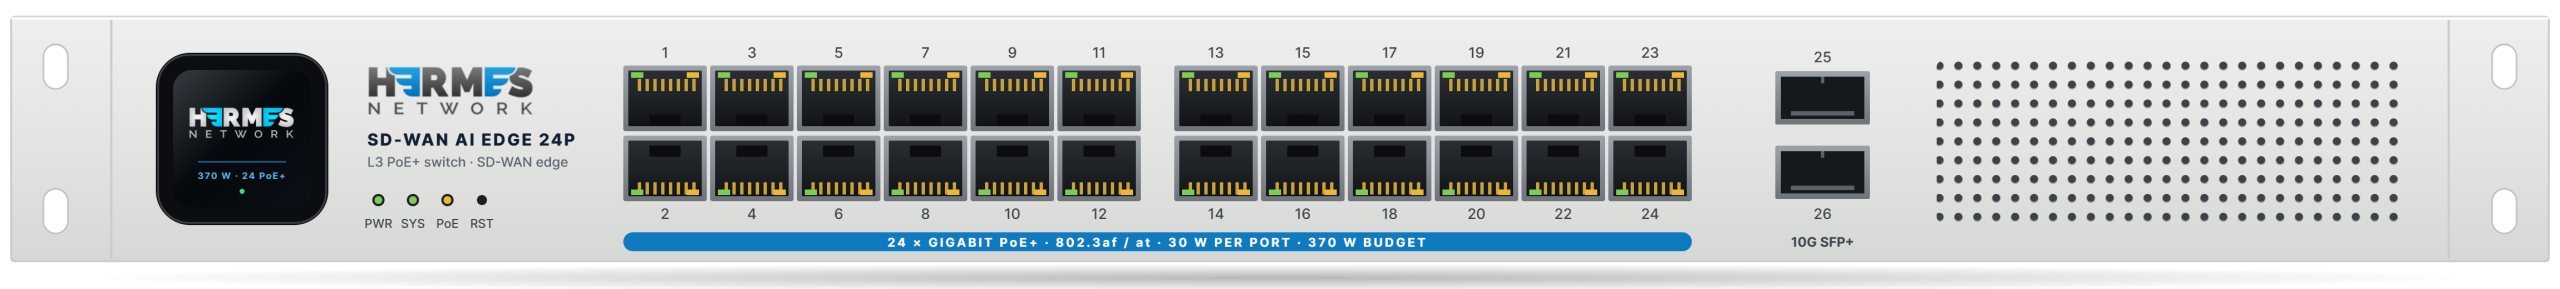
SD-WAN AI Edge 24P PoE

A Layer 3 PoE+ switch and an SD-WAN edge in one unit for larger sites.

Wi-Fi 7 Access Points

Wall, desktop and ceiling access points, managed from the same Orchestrator.

FAQ

SASE and Zero Trust FAQ

Can’t find your answer? Our solutions architects are happy to help

SASE (Secure Access Service Edge) combines wide-area networking and network security into one cloud-delivered service. Users and sites connect through the same fabric, and the same security policy follows them wherever they are.

A traditional firewall trusts whatever is inside the network perimeter. Zero Trust trusts nothing by default: every connection is verified against identity and device posture, and access is limited to what that role needs.

No. Hermes edges are deployed site by site and provisioned zero-touch, so you can start with one location and expand at your own pace while the Orchestrator keeps policy consistent.

On the Hermes edge at each site. Traffic is inspected locally and routed on the best available path, instead of being sent back to a distant data center first.

Everything is managed from the Hermes Orchestrator: sites, users, policies and security services, in one console.

See it on your network

Book a working session with a Hermes solutions architect —
we’ll model your sites in a Digital Twin first.