Solutions · Use Case

Compliance and Zero Trust access, built to be audited

Segmentation, least-privilege access and the logs and reports your auditors ask for, managed from one platform

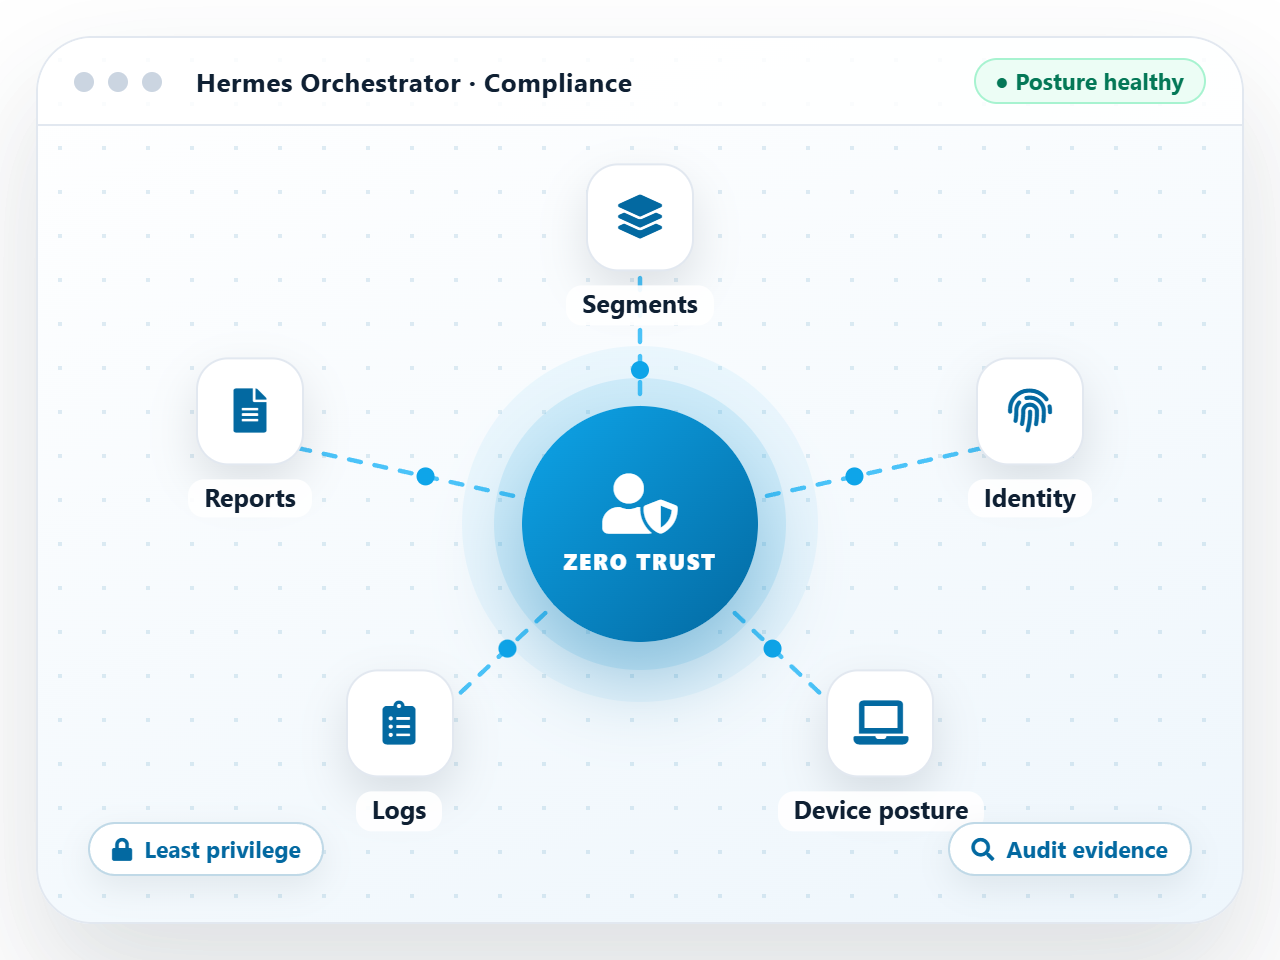
Hermes diagram: compliance zero trust access
Why it matters

Compliance as a state, not a snapshot

Audits ask the same questions again and again: which systems hold sensitive data, who can reach them, and how do you know nothing else can. On a flat network spread across many sites, answering those questions means weeks of evidence gathering, and the answer is out of date as soon as it is written.

Hermes builds the answers into the network. Sensitive systems sit on their own segments, access is granted by identity and role, and every site logs to one place. Your team can show what is isolated and who has access at any time, instead of rebuilding the picture before each audit.
At a glance
Segmentation that contains scope
Least-privilege access by default
Central logs and reports on demand
Continuous posture, not a yearly snapshot
Capabilities

Built to be audited

The controls auditors ask about, on every site

Segmentation

Contain scope by isolating sensitive systems on their own segments.

Least privilege

Zero Trust access as the default, with every connection verified by identity.

Device posture

Check device health before granting access, through the 360 Guard agent.

Evidence on demand

Central logs and reports from every site, ready for your reviews.

Data protection

AI-assisted DLP helps keep regulated data from leaving.

Safe change

Test policy changes in the Digital Twin before they reach production.

How it works

From flat network to Zero Trust

1

Map

Identify sensitive systems, users and devices across your sites.

2

Segment

Model segments and access policy in the Digital Twin first.

3

Enforce

Apply least-privilege access from the Orchestrator to every site.

4

Prove

Pull logs and reports whenever an auditor asks.

Hardware

Runs on Hermes hardware

Every Hermes device is provisioned zero-touch and managed from the same Orchestrator

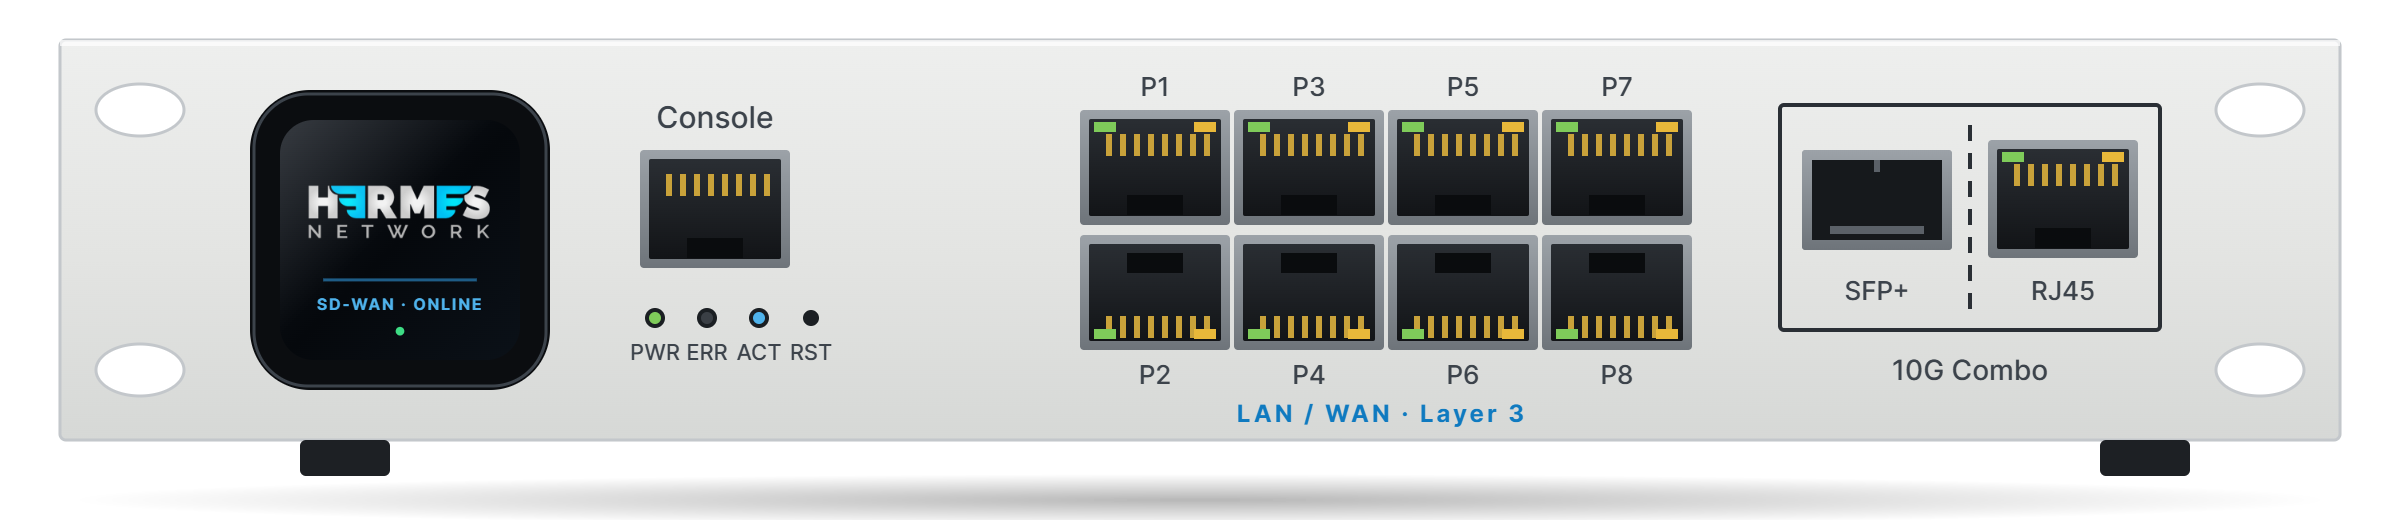
SD-WAN AI Edge Desktop

Branch SD-WAN, Layer 3 switching and edge AI in a compact desktop appliance.

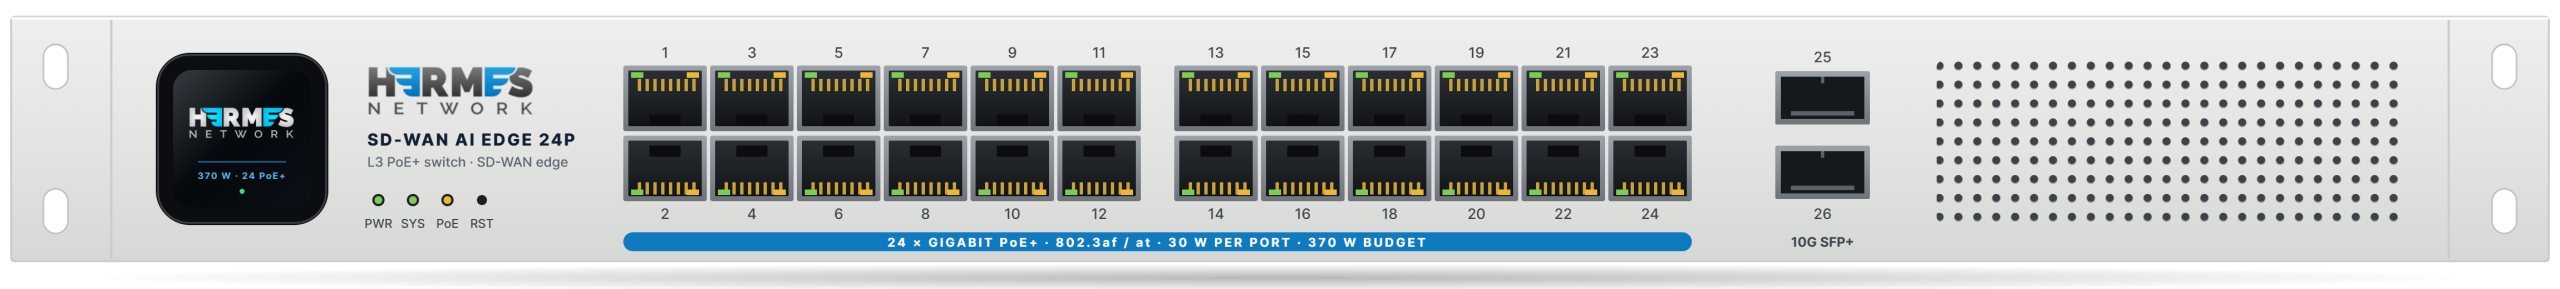
SD-WAN AI Edge 24P PoE

A Layer 3 PoE+ switch and an SD-WAN edge in one unit for larger sites.

Wi-Fi 7 Access Points

Wall, desktop and ceiling access points, managed from the same Orchestrator.

FAQ

Compliance and Zero Trust FAQ

Can’t find your answer? Our solutions architects are happy to help

Zero Trust access means no user or device is trusted because of where it sits on the network. Every connection is verified against identity and device posture, and access is limited to what that role needs.

Placing sensitive systems on their own segments limits which parts of the network can reach them. That makes the scope of an audit smaller and easier to explain.

Hermes provides the technical controls that many frameworks ask about: segmentation, least-privilege access, device posture checks, and central logs and reports. Talk to our team about the specific frameworks you report against.

Yes. Every site logs centrally to the Hermes Orchestrator, so reports can be pulled when they are needed instead of gathered by hand.

Yes. Changes can be modelled in the Hermes Digital Twin before they are applied, so you can see the effect on access before it goes live.

See it on your network

Book a working session with a Hermes solutions architect —
we’ll model your sites in a Digital Twin first.