Solutions · Industry

Government networking built on Zero Trust

Least-privilege access, segmentation and central visibility for agencies, plus a Federal MSP/MSSP path for the partners who serve them

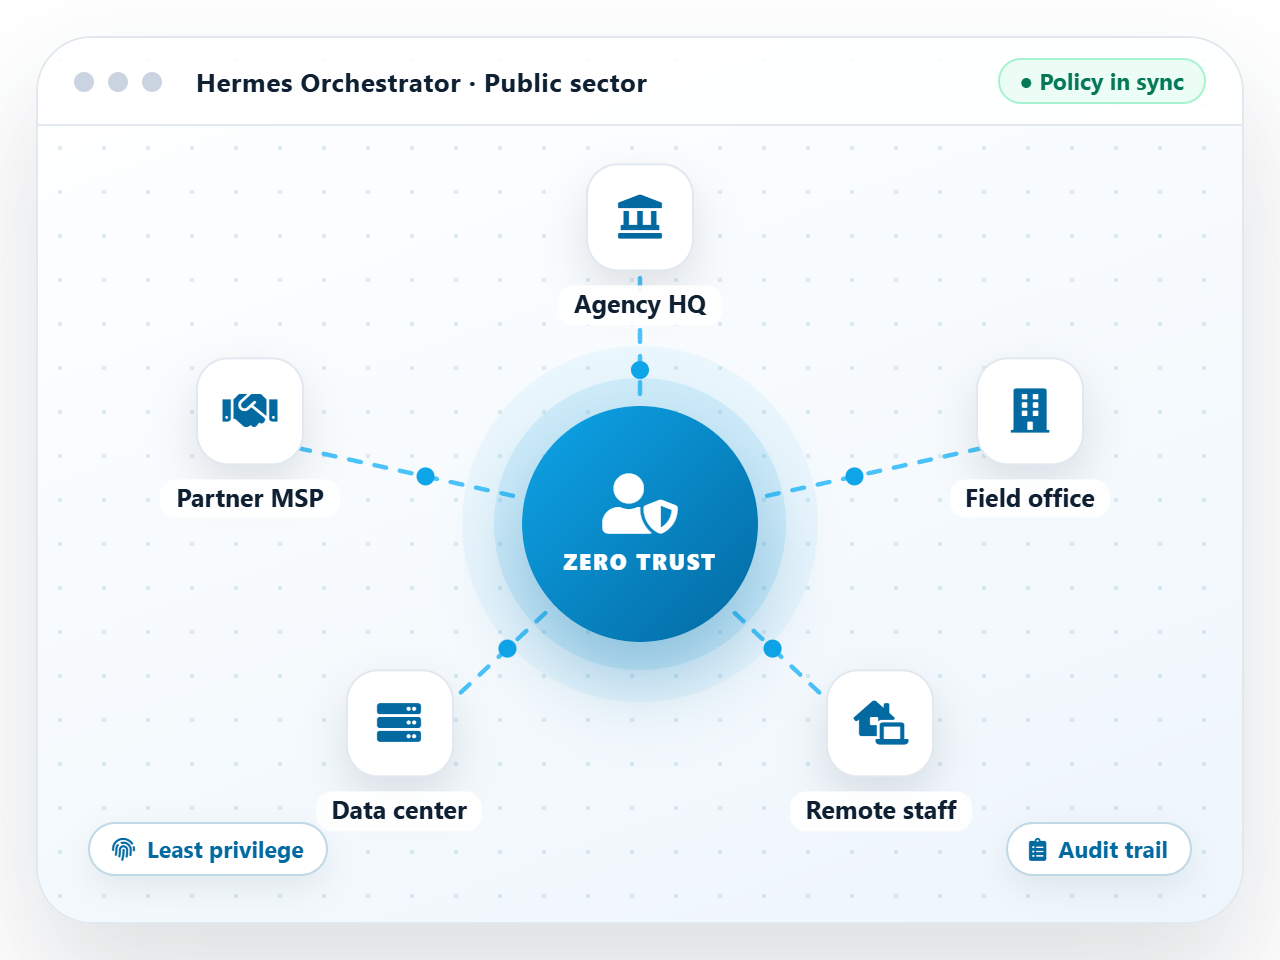
Hermes network diagram for government federal
The challenge

Mission first, security always

Agencies run offices, field sites and remote teams that all need secure, reliable access to systems and data. Security requirements keep rising, while IT teams are asked to do more with the same resources and keep the mission moving.

Hermes applies Zero Trust principles across every site: no user or device is trusted by default, access is granted by identity and role, and traffic is inspected at the edge. Policy is managed centrally in the Orchestrator, and agencies can work directly with Hermes or through a Federal MSP/MSSP partner.
At a glance
Least-privilege access by default
Segmentation across offices and field sites
Central logs and audit trail
Delivered directly or through federal partners
How Hermes fits

How Hermes fits government

Built for agencies, field operations and the partners who support them

Zero Trust access

Least privilege as the baseline, with every connection verified by identity.

Segmentation

Separate systems and users so access is limited to what each role needs.

Federal partners

A dedicated Federal MSP/MSSP program for partners serving agencies.

Data and policy control

Decide where data and policy live across your sites and cloud.

Threat detection

Inline IDS/IPS and live threat intelligence across every site.

Audit trail

Central logs and reports from every site for your security reviews.

How it works

From first site to Zero Trust

1

Assess

Map users, devices and systems, and model the target policy in the Digital Twin.

2

Deploy

Install Hermes edges zero-touch at offices and field sites.

3

Enforce

Apply least-privilege access and segmentation from the Orchestrator.

4

Monitor

Watch activity and threats across every site from one console.

Hardware

Runs on Hermes hardware

Every Hermes device is provisioned zero-touch and managed from the same Orchestrator

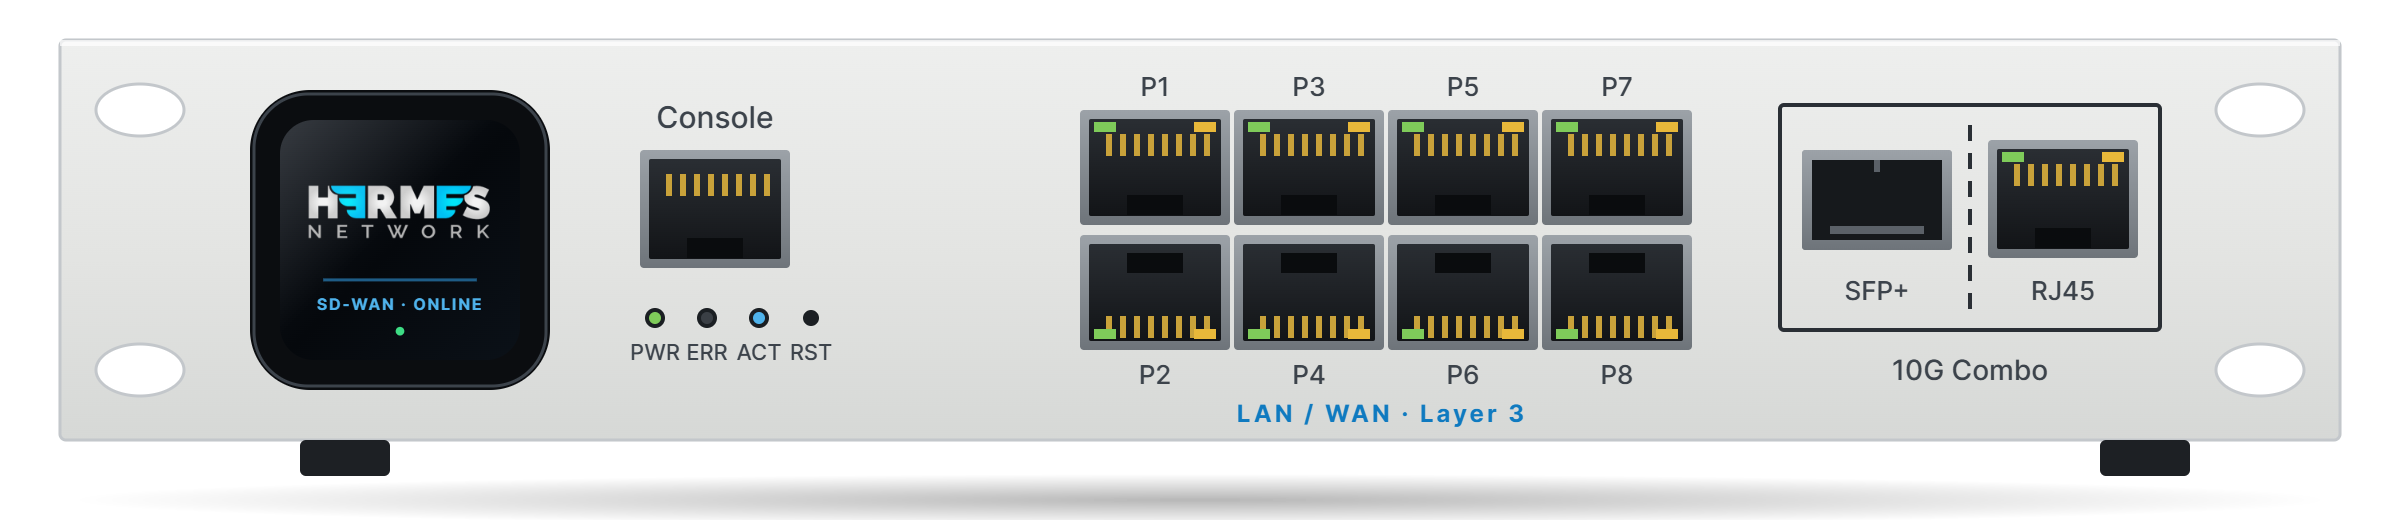
SD-WAN AI Edge Desktop

Branch SD-WAN, Layer 3 switching and edge AI in a compact desktop appliance.

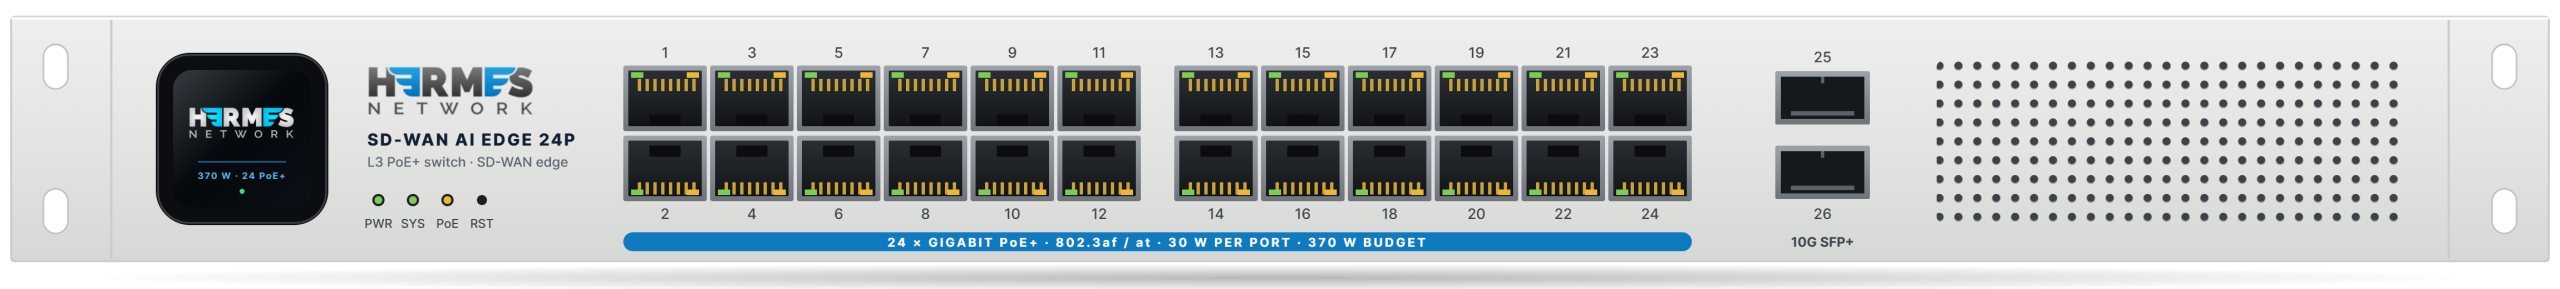
SD-WAN AI Edge 24P PoE

A Layer 3 PoE+ switch and an SD-WAN edge in one unit for larger sites.

Wi-Fi 7 Access Points

Wall, desktop and ceiling access points, managed from the same Orchestrator.

FAQ

Government networking FAQ

Can’t find your answer? Our solutions architects are happy to help

No user or device is trusted because of where it sits on the network. Every connection is verified against identity and device posture, and access is limited to what that role needs.

Yes. The Hermes Federal MSP/MSSP program supports partners who deliver and manage networks for public-sector customers.

Hermes provides least-privilege access, segmentation, and central logs and reports that your team can use in its security and compliance reviews. Talk to our team about the frameworks you need to meet.

No. Hermes devices are provisioned zero-touch. Someone on site connects power and the internet line, and the site comes online with central policy.

Every site, user and policy is managed from the Hermes Orchestrator, in one console.

See it on your network

Book a working session with a Hermes solutions architect —
we’ll model your sites in a Digital Twin first.