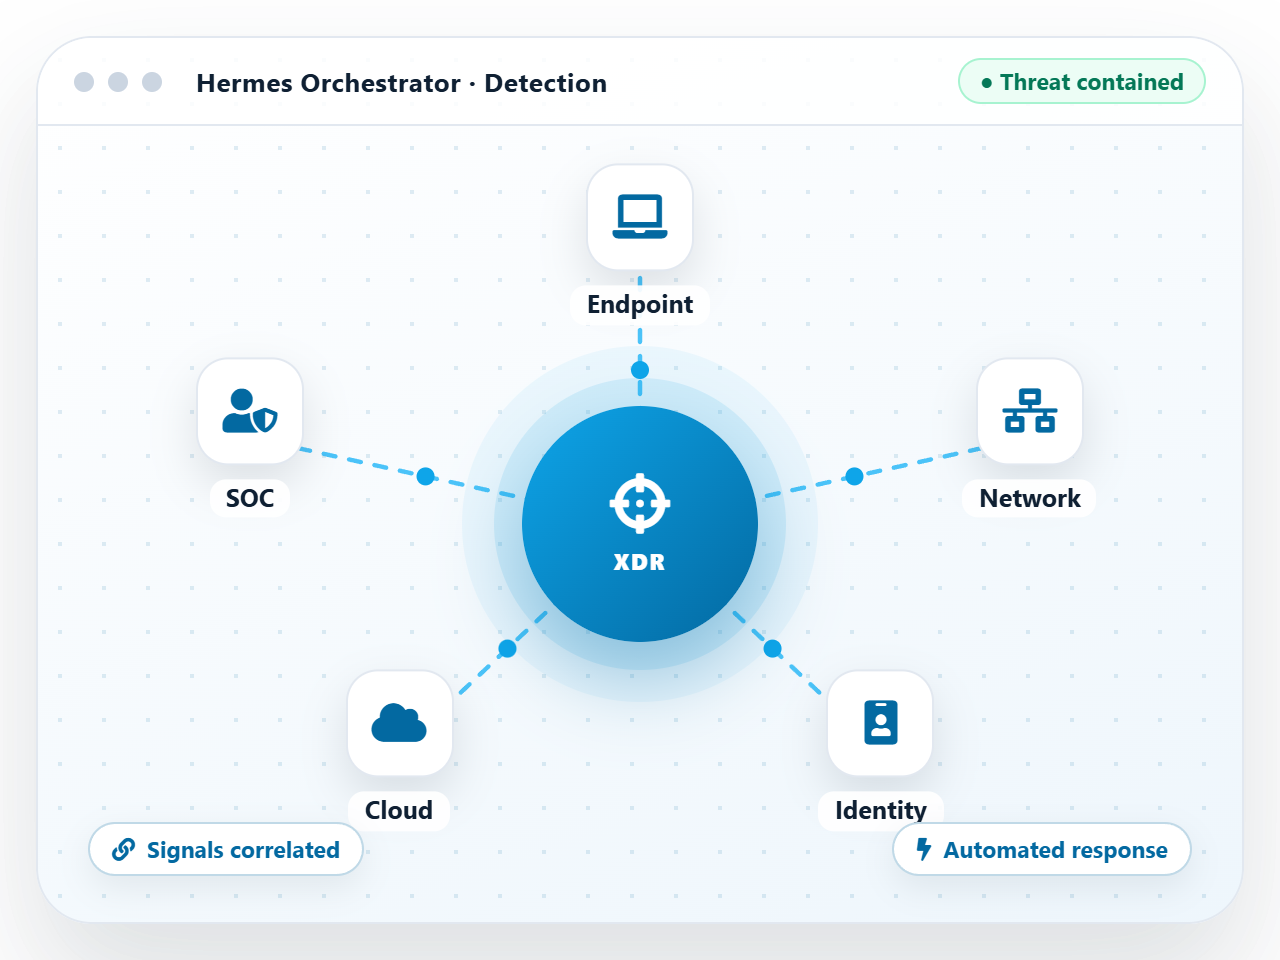
Attacks rarely show up in one place. A phishing email lands on a laptop, a stolen credential is used from an unusual location, and unusual traffic leaves a branch. Each tool sees one piece, and security teams lose time stitching alerts together while the attacker moves on.
Hermes brings those signals together. Endpoint, network and identity events are correlated into a single, prioritised alert with the context needed to act. Response can be automated to contain a threat in seconds, and teams that prefer it can have the Hermes SOC run detection and response around the clock.