

Next-Gen Firewall at every edge
Application-aware, identity-aware deep packet inspection at the branch — centrally policy-managed, never a set of one-off boxes
Application-aware, identity-aware deep packet inspection at the branch — centrally policy-managed, never a set of one-off boxes
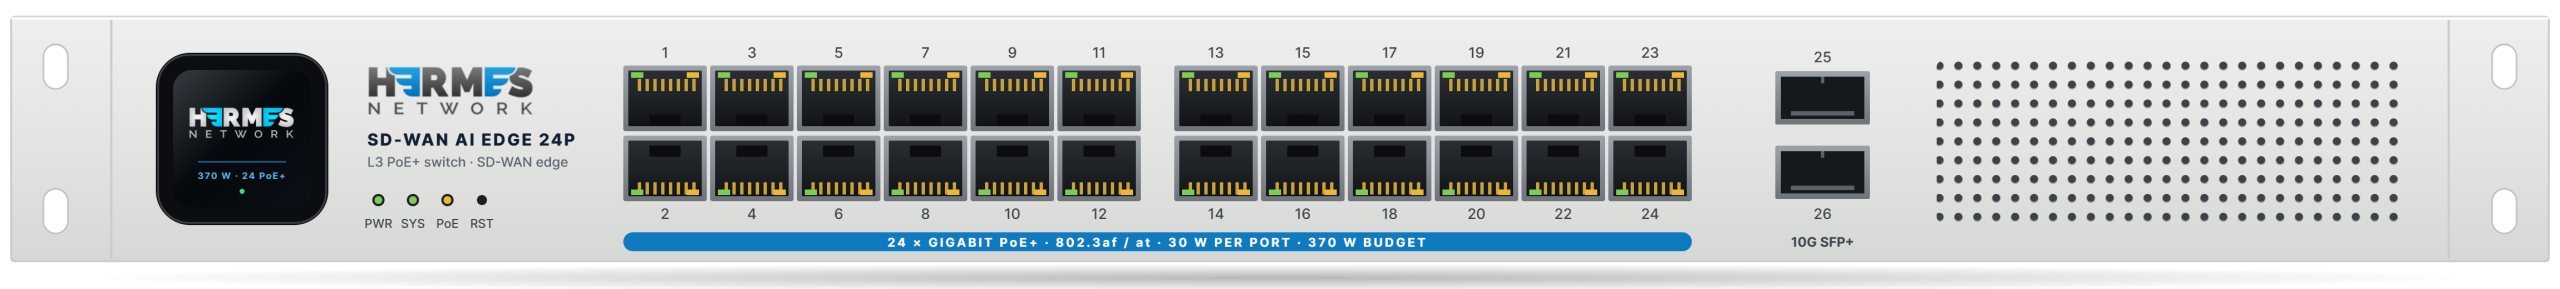
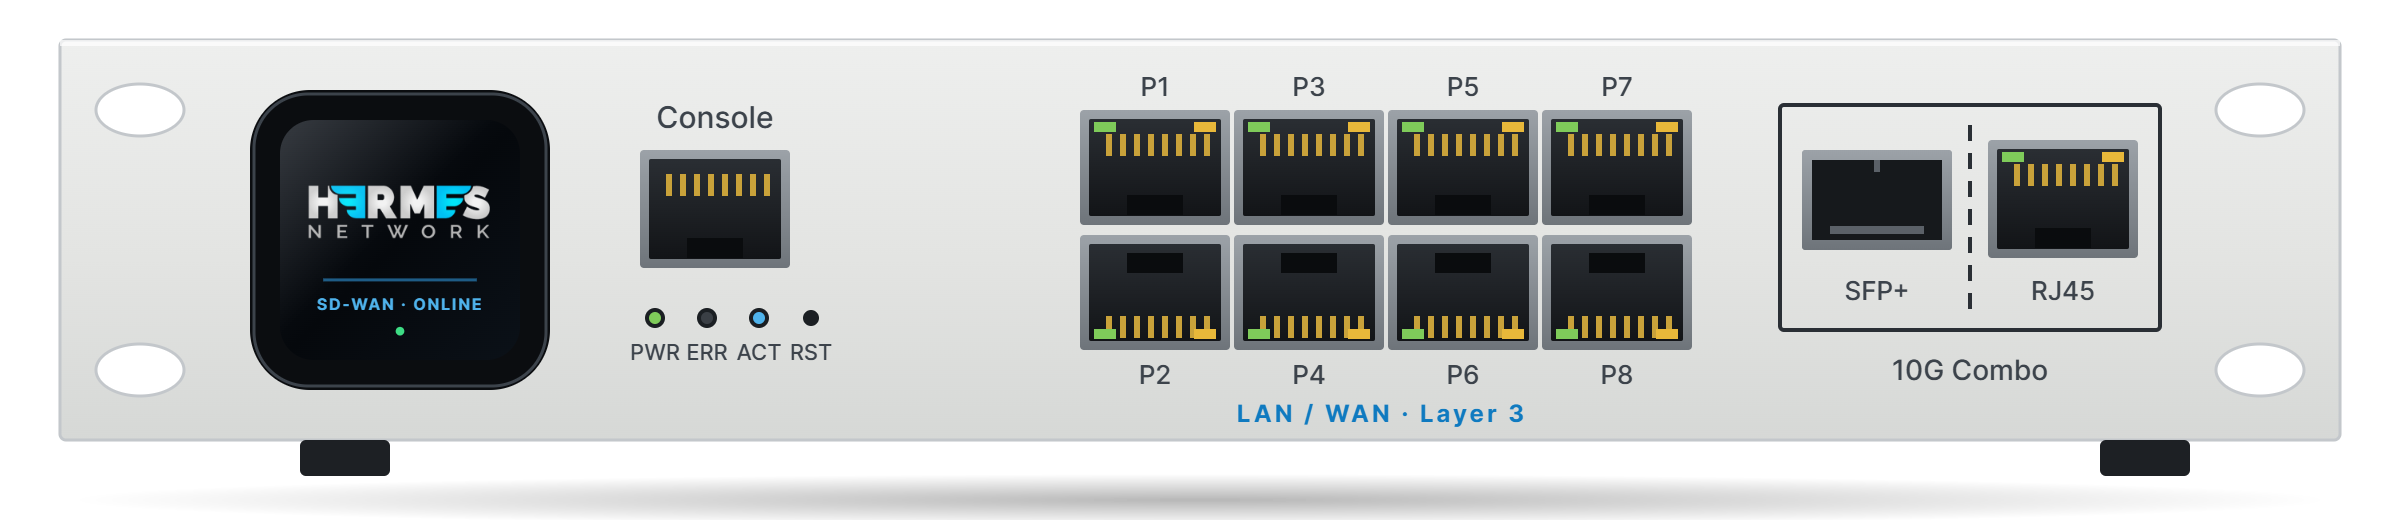
A traditional firewall decides on ports and IP addresses. Modern traffic does not fit that model: hundreds of applications share the same web ports, users move between offices and home, and attackers hide inside allowed traffic.
A next-generation firewall (NGFW) inspects the traffic itself. Hermes identifies the application and the user behind every flow and applies policy to them, at every site. Because the firewall runs on the Hermes edge and is managed from the Orchestrator, one policy is written once and enforced everywhere, instead of being maintained box by box.
The next-gen firewall runs on each SD-WAN AI Edge appliance. Hardware offload handles routing, NAT and tunnels, so the quad-core CPU is free for deep inspection
Firewall, segmentation and Layer 3 for the branch, with dual power.
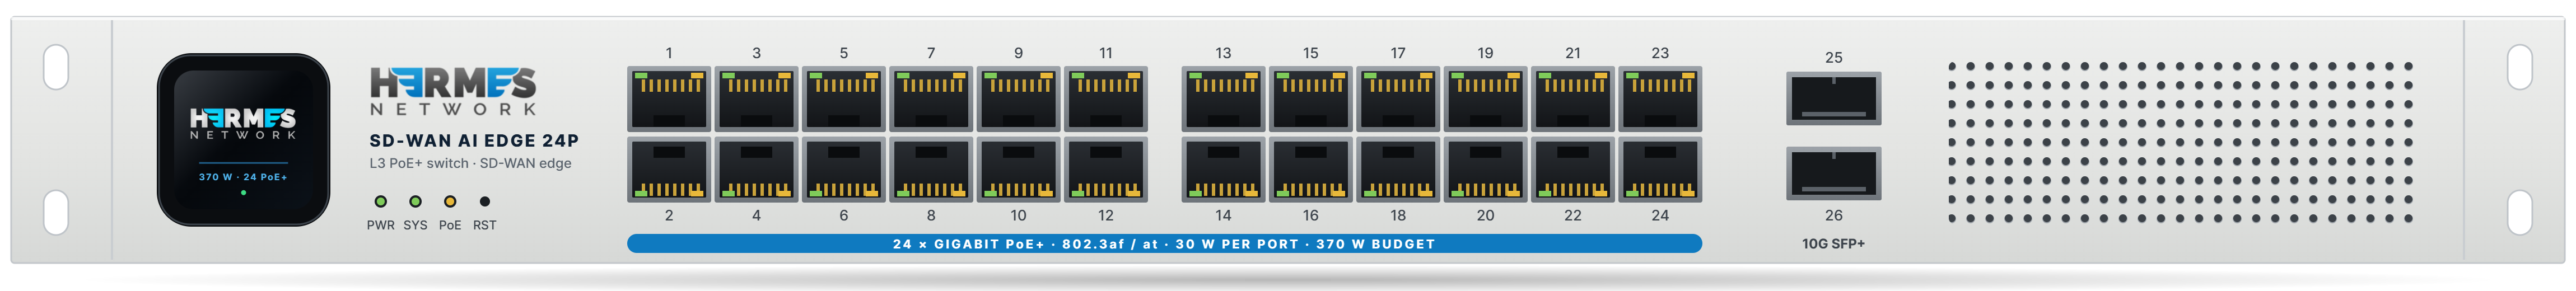
Firewall in front of 24 PoE+ ports: every camera, AP and phone is inspected.
Every Hermes product with key specifications, in English and Traditional Chinese.
The edge identifies the application and the user behind each flow.
Deep packet inspection checks the traffic against policy.
The flow is allowed, blocked or segmented by central policy.
Every decision is logged and searchable in the Orchestrator.
Can’t find your answer? Our solutions architects are happy to help
A next-generation firewall (NGFW) goes beyond ports and IP addresses. It inspects traffic to identify applications and users, and applies policy to them, often together with intrusion prevention and threat intelligence.
On every Hermes SD-WAN AI Edge appliance, at the site itself. Traffic is inspected at the edge rather than sent to a distant cloud first.
Policy is written once in the Hermes Orchestrator and enforced on every edge, so sites stay consistent without one-off configuration.
Yes. Micro-segmentation separates systems and devices so an attacker who gets in cannot move freely across the network.
Yes. Every allowed and blocked flow is logged and searchable from the Orchestrator.
Book a working session with a Hermes solutions architect —
we’ll model your sites in a Digital Twin first.